The Sales Manager’s heart dropped. The devastating news delivered by the compliance and legal team was that the organization could not sign the business deal they had been working on over the past six months because the buyer was matched to an entity on a government denied parties list. If only they had been able to see this earlier in the sales cycle.
Screening for denied parties in Salesforce is rarely top of mind at the start of a deal, but this is exactly where such risks can be identified. What makes the loss in this story sting is that the situation is entirely preventable. As it turns out, companies can, indeed, spot high-risk deals the moment a prospect walks in the door, sparing sales the pain of investing time and resources pursuing a potential opportunity that can never move forward.
Your Customer Relationship Management (CRM) platform, not just Salesforce, is where every prospect enters your business. A compliance system that lives elsewhere is likely to delay risk visibility. The way to achieve early identification in a systematized manner is through continuous screening of transactions at the lead, contact and account level against sanctions lists directly in the Salesforce application.
Key Takeaways
- Screening for denied, debarred and blocked entities in Salesforce is a mission critical objective for organizations.
- The regulatory environment is moving faster than most review cycles. Organizations relying on periodic or disconnected screening are already behind.
- Emerging technologies have changed who your customers are and what they do with the technology you sell. AI-related export control rules mean screening requirements now reach different industries.
- The penalties for inadequate screening are large and well documented, and have affected companies small and large.
- Continuous rescreening is required throughout the sales lifecycle in order to ensure that you are still permitted to work with a prospect or customer that was initially cleared.
Why Screening for Restricted Parties is Important
Compliance regulations are stricter and more complex than they have ever been. Trade restrictions from agencies like the Office of Foreign Assets Control (OFAC) are expanding at a pace that manual compliance methods cannot keep up with. Doing business with an entity on those lists, even unknowingly, could lead to fines, revoked licenses, and, in serious cases, criminal charges.
This makes screening for denied, debarred, and blocked entities in Salesforce a mission-critical objective. Functions across the business (e.g., sales, procurement, HR, finance) play a role in your compliance, as each engages with third parties at different stages of the lifecycle. Staying compliant is a responsibility that export compliance and legal teams now share with everyone across the organization.
Since the goal of export controls and sanctions screening is to help ensure national security interests are protected, compliance covers controlled technology, sales and marketing, mergers and acquisitions, financial transactions, human resources, and access to corporate facilities and networks.
Official ‘Know Your Customer’ guidance reinforces this need for vigilance. The Bureau of Industry and Security’s (BIS) red flag indicators includes a checklist of warning signs such as a buyer found on a denied party list, they cannot provide sufficient information about end use, or they want to pay in cash when financing is the norm.
Image 1: Key BIS Red Flags / Risk Indicators
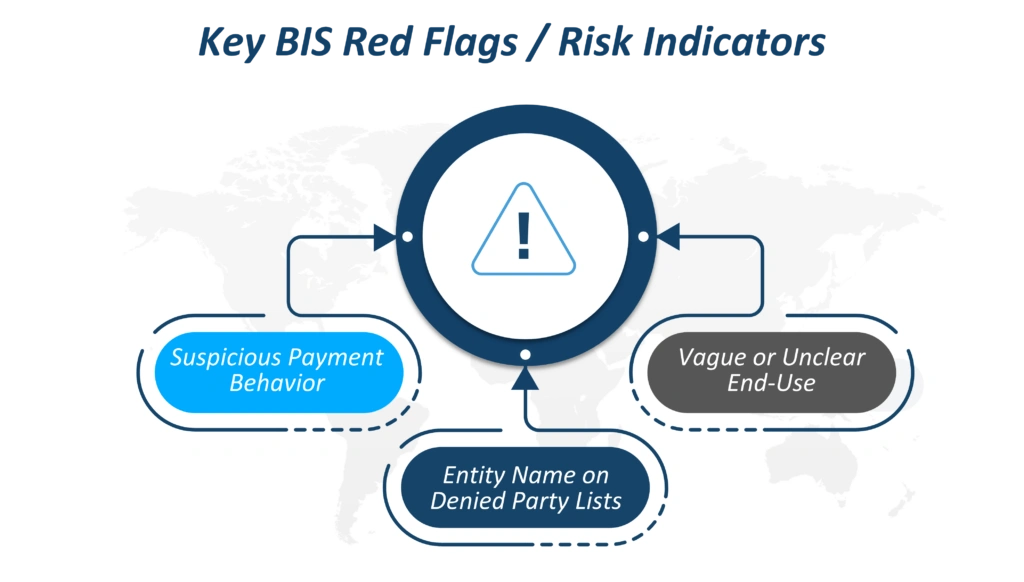
For these red flag indicators, sales teams are often best positioned to quickly identify the so-called ‘bad actors’ at the earliest stage, where prospects first enter the pipeline. As explored in Why Salesforce Works as a Compliance CRM, screening for denied parties in Salesforce enhances compliance from a disconnected checkpoint into a continuous, operational process—setting the foundation for managing today’s increasing regulatory complexity, emerging risks, and growing compliance demands.
Top Three Reasons Why Salesforce is Key for 3rd Party Compliance
Properly integrated, screening directly in Salesforce extends the effectiveness of the organization’s compliance initiatives. Here are the top three reasons to screen in Salesforce:
1: The Regulatory Environment Moves Faster Than Review Cycles
The pace of regulation has changed rapidly. OFAC and BIS have added entities to watchlists at rates higher than anything seen in previous decades. Geopolitical events have catalyzed sanctions programs virtually overnight. Rules like the OFAC 50% ownership rule and BIS 50% Affiliates guidance increase screening complexity. Forced labor laws (e.g., Uyghur Forced Labor Prevention Act (UFLPA)) introduce new compliance obligations, and export licensing requirements are expanding.
Static compliance programs built for a more stable regulatory environment often lead to missed exposure. To avoid being caught off-guard, organizations must identify restricted parties with automated screening, when prospects first enter the sales cycle, and on an ongoing basis as they move through multiple points of engagement.
Why Salesforce Screening Matters
By integrating denied party screening directly into Salesforce, organizations can:
- Automatically screen records in real time as they are created
- Stay aligned with constantly changing regulations
- Eliminate gaps between regulatory updates and sales activity
This significantly reduces time spent on companies that pose compliance risks.

2: Emerging Technologies Create New Export Compliance Risk
The emergence of AI has had a knock-on effect on a number of industries, triggering rapid expansion of semiconductors export controls, dual-use technology restrictions, and stricter trade rules on commercial software, advanced manufacturing, and technology companies. These controls are being introduced to protect sensitive infrastructure such as photonics, robotics, and AI systems.
This has changed who your customers are, and what they can potentially do with products you sell. Screening requirements across industries have become more demanding, as organizations must now assess not only who they sell to, but also the end-use, who ultimately uses them (end-user), and whether technology transfer or deemed export risks apply. For example, a distributor approved years ago may now operate in a region that requires additional scrutiny, or an existing customer may become subject to export controls based on their end use or nationality.
Most organizations place their compliance focus at the point of contract or shipment. This means that the whole organization has already put in significant effort (Sales has turned the lead into an opportunity, finance has raised an invoice, manufacturing has built the product, legal has reviewed the terms) before screening is performed.
Why Salesforce Screening Matters
Salesforce is where opportunities are created and qualified. Embedding continuous monitoring at this level ensures that every new lead, contact, and account you create in Salesforce is screened at every stage as the pipeline investment increases.
With automated rescreening in Salesforce, compliance becomes a proactive, background process that guides sales activity and reduces the risk of unknowingly engaging with restricted entities tied to high-risk ecosystems. For example, a contact that initially cleared screening might later acquire a sanctioned subsidiary. Automated rescreening will notify you, enabling timely action.
For more detailed information, read Performing Effective and Comprehensive Denied Party Screening Within the Salesforce CRM.
3: The Operational Burden of Compliance is Surging
Compliance today is operationally intensive. Organizations face high volumes of global transactions, compliance risks that are less visible, increasing audit and reporting expectations, and rising numbers of false positives, slowing sales. In addition, enforcement actions for non-compliance are increasing globally, with regulators placing greater scrutiny on how organizations manage sanctions and export control risks.
Average penalty values have risen consistently, and the cases that generate large fines share a common thread: sanctioned party data was already present within the organization’s systems but was not acted on appropriately.
Without the right screening tools, manual processes breakdown, introducing human error, creating friction for sales teams, and slowing legitimate business.
Why Salesforce Screening Matters
Building denied party screening directly into Salesforce workflows automates screening at scale—supporting rising transaction volume without increasing headcount. Robust solutions come with built-in audit trails that automatically capture screening activity and decisions, while AI-powered alert filtering capabilities help reduce false positives.
Benefits of Screening Throughout the Sales Cycle
Organizations across industries need to make sure they are not entering into business with a denied or restricted party, both at home and abroad. In addition to meeting regulatory compliance requirements, screening also helps minimize operational disruptions, penalties and adverse media coverage.
For sales, this means being able to identify denied parties throughout the sales cycle—and at the lead, contact and account levels—because additions to watch lists maintained by governments and international bodies are continuous. This maximizes sales’ time on legitimate opportunities.
“Thanks to the efficiency and robustness of Descartes Visual Compliance, I’d put our compliance program up against literally any company of our size in the world right now. Plus, with Salesforce integration, we can dynamically screen lead lists, web-driven subscribers, and existing customers to streamline the sales response process and accelerate the sales cycle.”
Paul Lucchese, Vice President & General Counsel, EDB – Read the full EDB Case Study
How To Make Salesforce Your Compliance Control Layer
It may seem daunting to introduce new compliance processes, but deploying denied party screening in Salesforce is a practical and achievable step. When aligned with how your sales teams use Salesforce and our organization’s compliance requirements, screening becomes part of everyday workflow.
The following steps outline how organizations can deploy comprehensive denied party screening solutions like Descartes Visual Compliance within Salesforce and establish it as the operational control layer for compliance:
- Embed Screening at the Point of Entry
Configure screening to trigger automatically when a new lead, contact, or account is created within your Salesforce CRM. The moment a prospect enters your system, you know they have been screened and whether it is safe to proceed or if they have been flagged for further review.
- Enable Continuous and Automated Rescreening
Descartes Dynamic Screening means rescreening runs automatically when watch lists are updated. This continuous screening means that a contact that has been initially cleared and then appears on a sanctions list gets automatically flagged without manual effort before any further sales interaction.
- Integrate Compliance into Sales Workflows
Screening in Salesforce doesn’t mean having to switch windows, use separate systems or wait for compliance reviews. Sales reps see what they need within Salesforce and this ease of use helps to improve adoption and support compliance practices.
Image 2: Salesforce Screening Workflow

- Reduce Operational Friction with Automation
False positives are one the biggest bottlenecks for compliance programs and can slow the pipeline. When teams are pressured to clear false positives quickly, they can rush the process and may miss genuine flagged companies. With Descartes you can fine tune screening parameters and automated escalation routes without requiring manual triage, which lowers false positives.
- Maintain a Complete Audit Trail
When facing a regulatory review, you need a flawless audit trial. You must be able to prove exactly who was screened, against which lists these checks were carried out, and what the final results were. With Descartes DPS for Salesforce these comprehensive records are created automatically.
- Align Sales and Compliance Around a Single System
When screening lives in Salesforce, both the compliance team and the sales team can view the status of a prospect customer or partner in real time. This integration ensures there are no information gaps and that all decisions are visible to both teams.

How can Descartes Help?
Descartes provides an industry-leading suite of denied party screening and third party risk management solutions that can be seamlessly integrated with Salesforce, sometimes in under an hour.
Descartes Visual Compliance solutions are flexible and modular, allowing organizations to pick the specific functionality and content they need for their particular compliance needs and scale up later when necessary.
Find out what our customers are saying about Descartes denied party screening on G2, an online third-party business software review platform. Additionally, you can read this essential buyer’s guide to denied party screening to help you select a solution that fits your needs.
Frequently Asked Questions About Screening for Denied Parties in Salesforce
Frequently Asked Questions
What is restricted party screening in Salesforce?
Restricted or denied party screening in Salesforce is the process of automatically checking leads, contacts, and accounts against global sanctions and restricted party lists (e.g., OFAC, BIS, EU) directly within the CRM to prevent non-compliant business relationships.
Does Salesforce support compliance with OFAC 50% rule?
Salesforce does not natively support compliance with the OFAC 50% Rule or provide built-in sanctions screening. However, it supports integrations with third-party trade compliance platforms like Descartes Visual Compliance. These solutions enable real-time OFAC screening directly within Salesforce, including the ability to comply with complex requirements like the OFAC 50% Rule, where entities owned 50% or more by sanctioned parties must also be treated as restricted.
How often should Salesforce records be rescreened?
Ideally, Salesforce records are rescreened continuously to ensure alignment with frequently updated sanctions lists and regulatory data. Continuous, automated rescreening allows organizations to identify new risks as they emerge and ensures that previously cleared records remain compliant throughout the sales cycle.
However, the appropriate rescreening frequency ultimately depends on an organization’s risk landscape, including factors such as industry, geographic exposure, and regulatory requirements. Robust screening solutions provide the flexibility to schedule rescreening at different intervals—such as daily, weekly, or event-triggered (e.g., data changes or list updates)—to match these varying risk profiles.
Is Salesforce ITAR compliant?
Salesforce can support ITAR compliance, but compliance depends on configuration, data handling practices, and use of compliant integrations. Organizations must implement controls such as access restrictions, encryption, and audit tracking.
How does Salesforce screening improve third-party risk management?
Salesforce Screening improves third-party risk management by embedding compliance directly into daily business workflows. By screening leads, contacts, and accounts at the point of entry—and continuously thereafter—organizations can:
- Identify high-risk or restricted parties early in the sales cycle
- Prevent non-compliant relationships from entering the pipeline
- Provide real-time visibility into third-party risk across sales, procurement, and finance
- Maintain consistent screening and audit trails for due diligence